AI-Powered Windows 11 System Maintenance & Repair Tool: Fevren AI Maintenancer v1.7.0
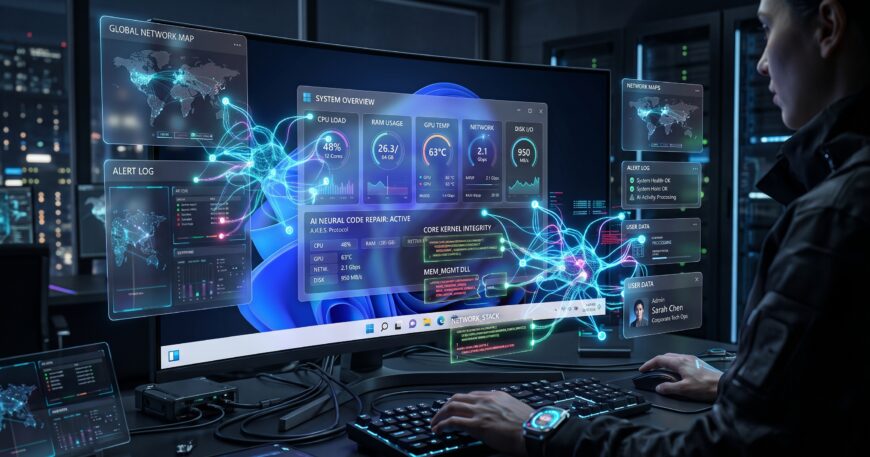
Far beyond superficial cleaners: an enterprise Windows 11 diagnostics and repair platform that scans your OS across 32 ultra-deep kernel, hardware, and binary BSOD (.dmp) telemetry vectors, pinpoints root causes with Google Gemini 4 Carbon (Medium Thinking), and executes repairs via a 12-Module Licensed Surgical Playbook Arsenal and a 15-Step Autonomous ReAct Agent with automatic post-reboot health verification.
1. 🧠 Google Gemini 4 Carbon (Medium Thinking) & Binary Root-Cause Engine
Fevren AI Maintenancer v1.7.0 Enterprise powers its diagnostics, live system consultant, and 15-step autonomous repair loop with Google Gemini 4 Carbon (thinkingLevel: "medium"). Rather than just reading event logs, it correlates binary crash dump stacks with hardware bus resets and OS subsystem states:
🔬 Binary .dmp Forensics & Medium Thinking
Gemini 4 Carbon cross-reasons PAGEDU64 binary minidump .sys stacks, WHEA hardware faults, NVMe Event 129/153 bus resets, and WMI/CBS dependencies to target the true root cause.
⏱️ Adaptive Timeouts & Dual-Encoding Stream
Grants 8–15 minute adaptive timeouts for DISM, SFC, and Winget repairs, decodes live UTF-16LE / UTF-8 streams cleanly, and automatically runs verification_step audits after each fix.
🛡️ Multi-Layer Rollback & Post-Reboot Audit
Backs up Registry keys + Service startup types + hosts file alongside a System Restore Point before any change. Reboot-pending repairs are tracked and verified on the Dashboard after restart.
2. 🛠️ 12-Module Licensed Surgical Deep Repair Playbook Arsenal
In v1.7.0, the Surgical Deep Repair Arsenal expands to 12 deterministic playbooks. During your active 2-hour diagnostic session (or invoked directly by the 15-step ReAct agent via tool_playbook), all 12 modules run with zero extra credits deducted:
salvagerepository) and removes conflicting phantom PnP devices.
Audiosrv, AudioEndpointBuilder, and MMCSS multimedia scheduling services.
reagentc).
w32tm clock resync and refreshes corrupted SSL/TLS root certificate stores.
0xc000007b and missing VCRUNTIME140.dll crashes via official Microsoft Winget runtimes (x64/x86 + Edge WebView2).
3. 🤖 15-Step Autonomous ReAct Agent, Playbook Orchestration & Live Consultant
- 🔄 15-Step ReAct Loop with
tool_playbook: For complex kernel faults, the Gemini 4 Carbon agent executes up to 15 inspect-repair-verify steps, combining custom PowerShell scripts with direct calls to the 12 tested surgical playbooks (tool_playbook). - 🧭 Live Mid-Run User Guidance: While terminal output streams in real time (
output_chunk), users can steer the agent mid-session without interrupting execution (e.g., “Leave SQL Server untouched, only reset the network stack and VC++ runtimes”). - 💬 Fevren AI Live System Consultant: Chat directly with an AI consultant that already knows your hardware specs and 32-vector health panorama.
- 🔁 Post-Reboot Health Verification: Repairs requiring a restart (disk Dirty Bit
chkdsk, Winsock/TCP-IP reset, pending SFC/DISM) are tracked and verified with one click on the Dashboard after reboot.
4. 🩺 32-Vector Ultra-Deep Kernel, Hardware & Binary BSOD Telemetry
Telemetry coverage in v1.7.0 expands to 32 ultra-deep vectors visualized in a 0–100 Health Score Panorama:
Kernel, Driver & System Layer (1–16)
- 1. Deduplicated Event Logs: Groups repetitive error storms into root incidents.
- 2. Reliability History (WER): App & hardware crash timeline.
- 3. Failed Auto-Start Services: Critical Windows services that stopped unexpectedly.
- 4. Faulty PnP Device Codes: Device Manager ConfigManager error codes.
- 5. Disk S.M.A.R.T. & Physical Health: NVMe/SSD/HDD wear & sector alerts.
- 6. BugCheck / BSOD Crash Codes: Kernel bluescreen parameter analysis.
- 7. Minidump Crash Inventory: Recent dump files and timestamps.
- 8. WMI Repository Consistency: Management infrastructure integrity check.
- 9. Ghost PnP Drivers: Phantom/disconnected hardware driver conflicts.
- 10. GPU TDR Display Resets: Display driver timeouts and DWM crashes.
- 11. Kernel Memory Bottlenecks: High RAM pressure & process analysis.
- 12. Power Plan & Thermal Throttling: CPU frequency throttling & power limits.
- 13. Audio Subsystem & Endpoints: Audiosrv & endpoint health.
- 14. CBS / WinSxS Image Integrity: DISM CheckHealth component store audit.
- 15. Windows Update Error History: Stuck KB packages & 0x800* codes.
- 16. Windows Defender & Security Posture: Real-time protection & signature status.
Network, App & Binary Forensics Layer (17–32)
- 17. Network Anomalies & DNS Latency: Resolution times and packet drops.
- 18. NIC Hardware & Winsock Health: Adapter errors and socket layer.
- 19. Crashing 3rd-Party Apps: Faulting module DLL analysis.
- 20. Failing Scheduled Tasks: Background tasks returning non-zero exit codes.
- 21. Print Spooler Queue: Locked print jobs and spooler status.
- 22. Orphan Startup Run Keys: Startup entries pointing to missing targets.
- 23. Pagefile & Virtual Memory: Commit charge pressure and pagefile usage.
- 24. Windows Recovery Environment (WinRE): Emergency recovery partition status.
- 25. IFEO & Restrictive Policies: Residual registry locks from malware.
- 26. VC++ & .NET Runtime Integrity: Game & enterprise library verification.
- 27. Binary BSOD Minidump (
.dmp) Stack Forensics (New): ParsesPAGEDU64binary headers to pinpoint offending 3rd-party.sysdrivers. - 28. NVMe / AHCI Bus Resets – Event 129/153 (New): Detects storage controller timeouts causing system freezes.
- 29. Kernel Non-Paged / Paged Pool & Handle Leaks (New): Identifies driver-induced kernel memory leaks.
- 30. WHEA-Logger Hardware Faults (New): Reports physical CPU cache, PCIe lane, and RAM ECC errors.
- 31.
Windows.edbBloat & Corrupt (.bak) Profiles (New): Flags oversized search indexes and broken user profiles. - 32. Laptop Battery Wear % (New): Compares Design Capacity vs. Full Charge Capacity.
5. 💳 Licensing, Cybersecurity & 2-Hour All-Inclusive Repair Window
- 1 Credit = Full 32-Vector Scan + 2 Hours of Unlimited Repairs: Spending 1 diagnostic credit unlocks a 2-hour all-inclusive repair session. Applying AI fixes, running any of the 12 Surgical Playbooks, launching the 15-Step ReAct Agent, and chatting with the Live System Consultant deduct zero extra credits.
- Hardened Cybersecurity Architecture: Locked to
127.0.0.1loopback, protected by 256-bitX-App-TokenAnti-CSRF headers, Anti-DNS Rebinding checks, andvalidatePowerShellSafety()destructive-command filtering. - Legal Evidence & Preventive Protection: EULA acceptance is sealed with an official TÜBİTAK Kamu SM RFC 3161 timestamp, and a Windows System Restore Point is created automatically before repairs begin.
⬇️ Download & Installation (v1.7.0)
v1.7.0 Installer (Setup.exe)
12.3 MB • Desktop shortcut, auto-elevation, and clean uninstaller.
💾 Download Setup (Recommended)
